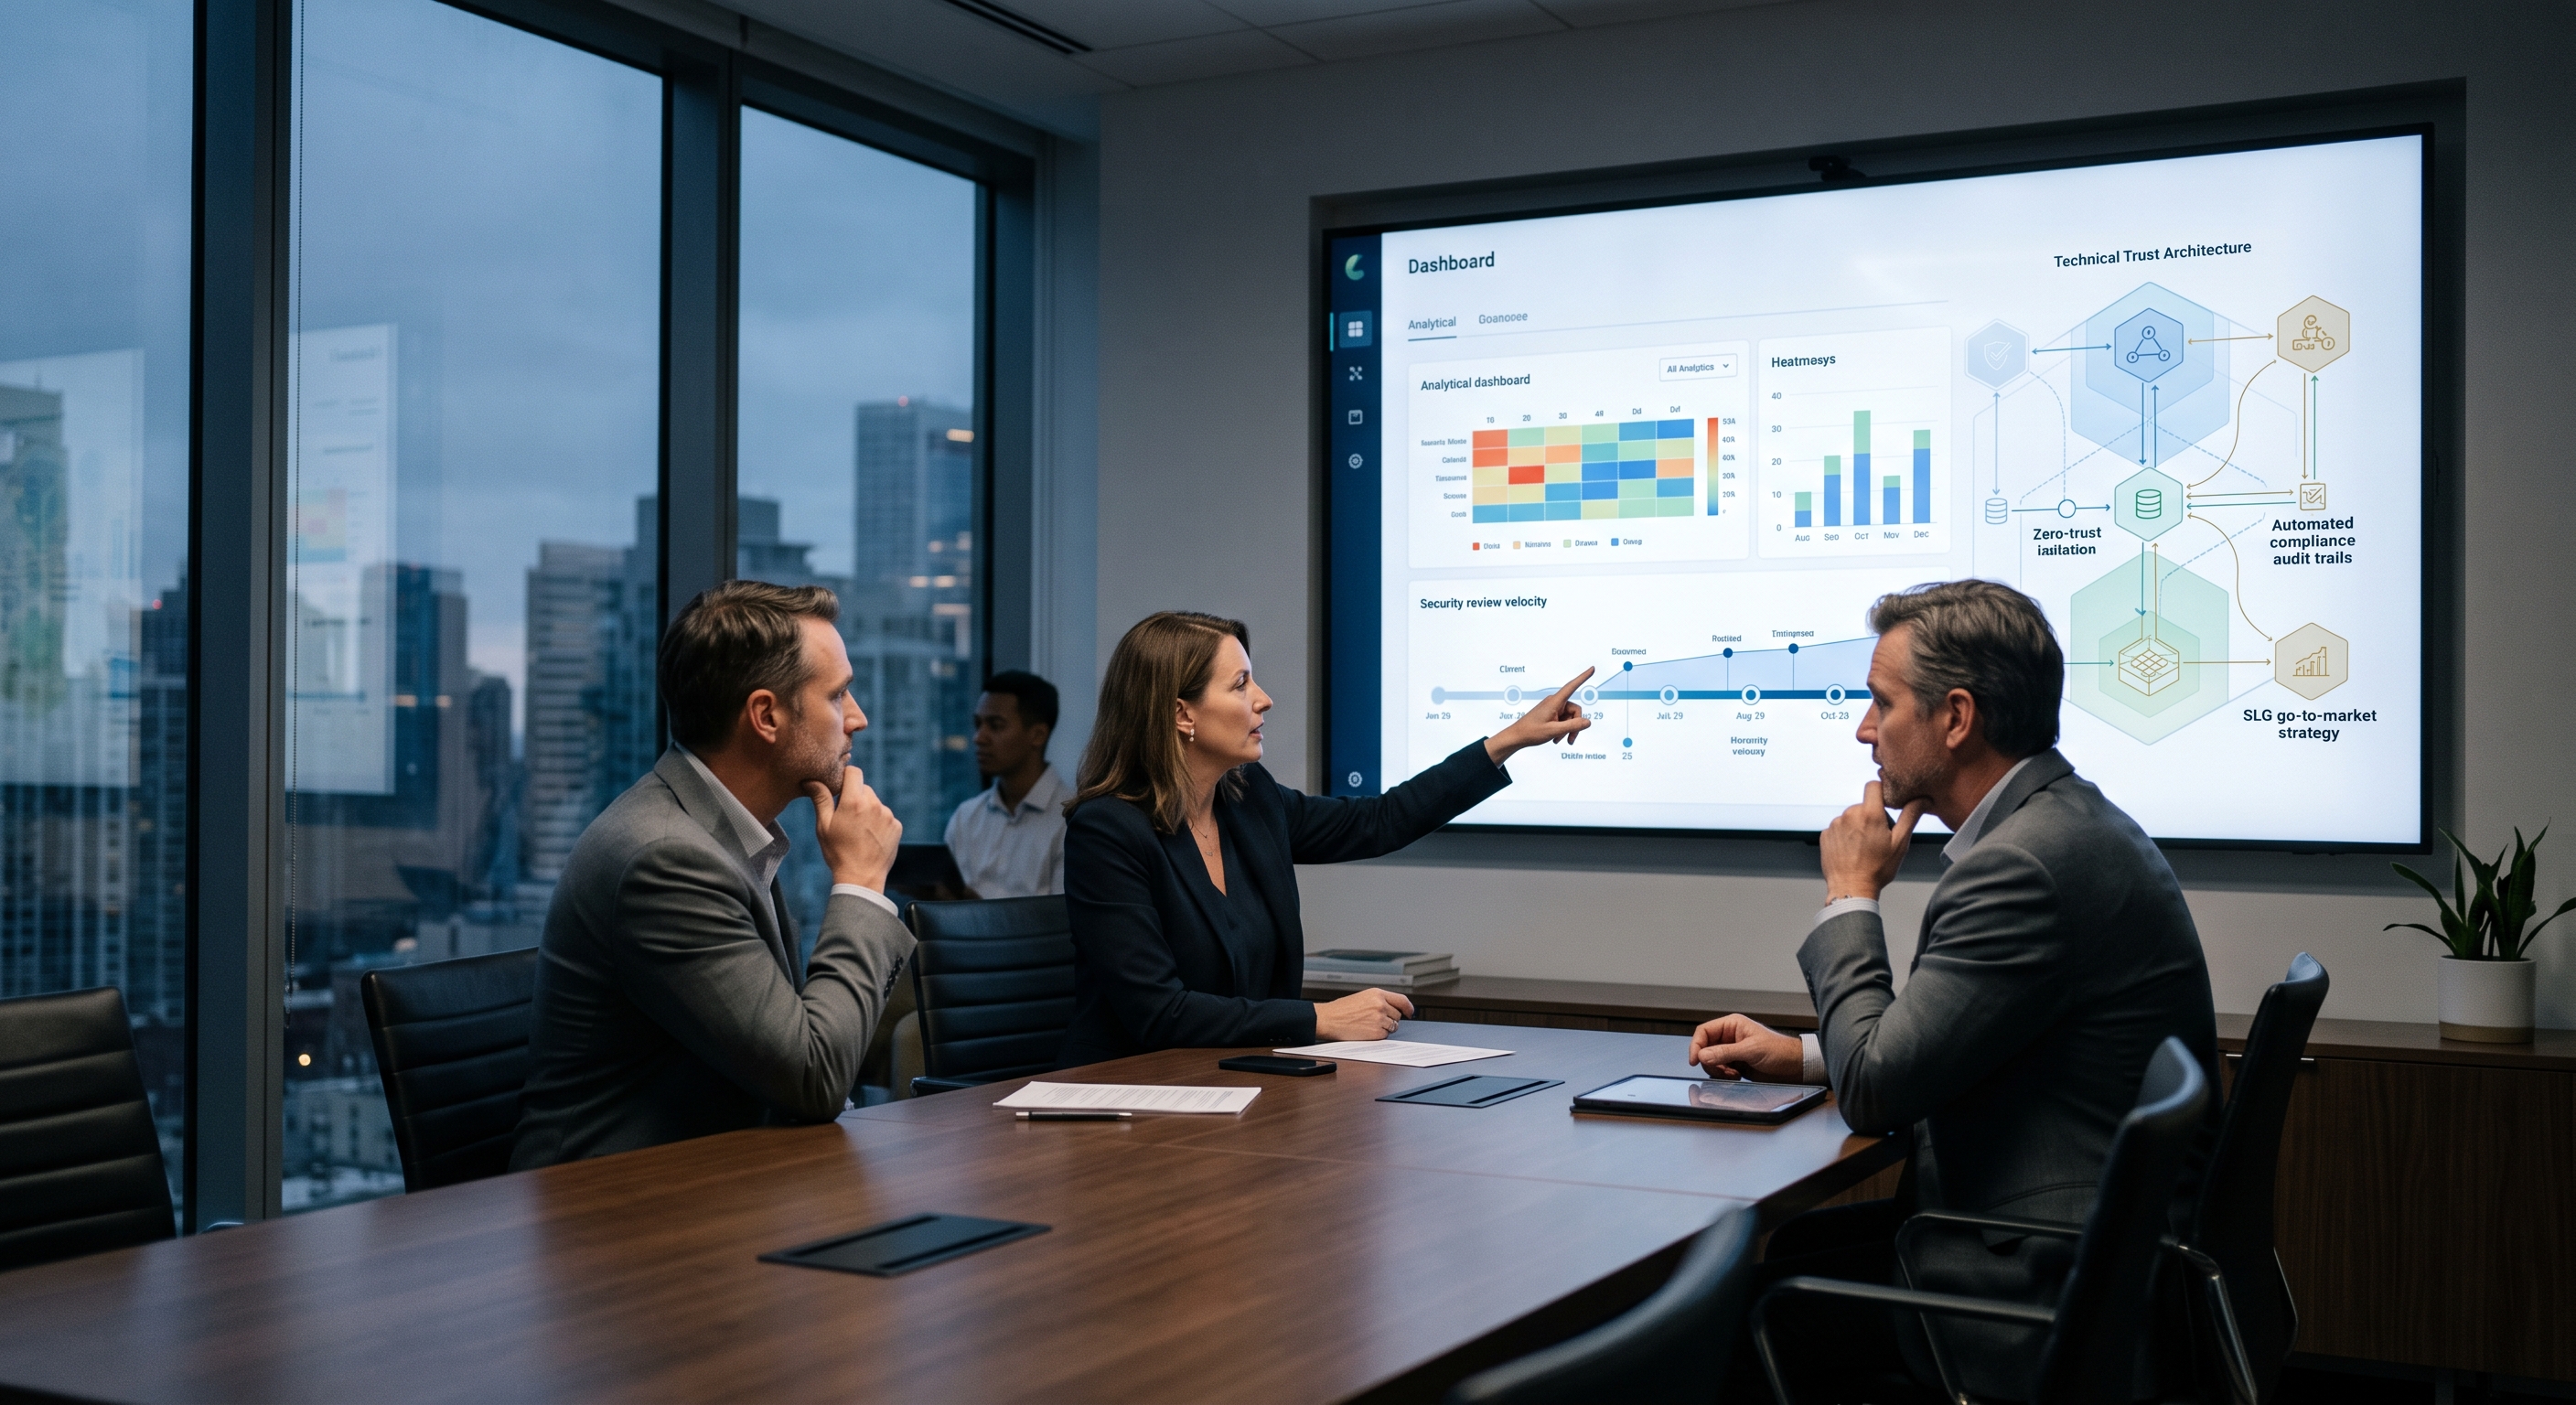
For enterprise SaaS, security is no longer something you explain after the demo. It can be one of the reasons a buyer takes the meeting in the first place.
- Product-Led Growth still works, but enterprise deals increasingly require more than product adoption.
- Security, privacy, AI governance, and data sovereignty can influence buying decisions much earlier.
- Security-Led Growth makes technical trust part of marketing and demand generation.
- A strong Trust Center can reduce the friction involved in enterprise evaluation.
- CISO-ready documentation helps internal champions defend a purchase.
- CMOs should measure security-review duration, deal slippage, sales-cycle length, and enterprise conversion.
- The goal isn't to replace PLG. It's to make enterprise software easier to trust and easier to buy.
Security-Led Growth: Why Enterprise SaaS Is Putting Trust Before Product
For years, Product-Led Growth gave SaaS companies a beautifully simple story.
Build a great product.
Let people try it.
Make adoption easy.
Then let usage spread through the organization until procurement eventually catches up.
That model still works.
But in enterprise SaaS, the environment around it has changed.
The problem isn't that enterprise buyers suddenly stopped caring about product experience. They haven't.
The problem is that a great product is no longer enough to get through the enterprise buying process.
Today, the buyer isn't just asking:
> "Does this solve my problem?"
They're also asking:
- Where does our data go?
- Who can access it?
- Is our data used to train AI models?
- Where is the data stored?
- What happens if our security team says no?
- Can our legal team approve the vendor?
- Can I give our CISO a credible answer?
- How quickly can we complete the security review?
And increasingly, those questions are appearing before the traditional product evaluation is complete.
That's where the idea of Security-Led Growth (SLG) becomes interesting.
SLG isn't about replacing product-led growth with security.
It's about recognizing that, for enterprise buyers, trust has become part of the product experience.
---
What Is Security-Led Growth?
Security-Led Growth is a go-to-market approach that makes security, privacy, compliance, data governance, and technical trust visible much earlier in the buying journey.
Instead of treating security as something Sales Engineering handles near the end of the deal, marketing makes it part of the company's market positioning from the beginning.
The basic shift is simple:
Old model:
Product → Adoption → Sales → Security Review → Procurement → Contract
Emerging model:
Trust → Evaluation → Product → Security Validation → Procurement → Contract
The second model doesn't mean every enterprise buyer starts with security.
It means that security should no longer be invisible until the buyer asks for it.
For a $50,000, $100,000, or $500,000+ annual contract, buyers aren't just buying software.
They're taking on organizational risk.
Your marketing needs to acknowledge that.
---
Why Product-Led Growth Gets Harder at Enterprise Scale
I'm not convinced the right conclusion is that "PLG is dead."
That's too simplistic.
PLG remains extremely powerful for product discovery, user activation, expansion, and reducing the cost of initial adoption.
But there is a point where the mechanics of product adoption collide with enterprise governance.
A developer can sign up for a new tool in minutes.
Getting that tool approved across a regulated enterprise can take weeks or months.
That's the gap.
The person who loves your product might not be the person who can approve it.
And the person who can approve it might never have heard of your company before the security questionnaire arrives.
This creates one of the most frustrating situations in enterprise SaaS:
The product has won the user, but the company hasn't won the account.
That's a marketing problem as much as it is a sales problem.
---
The Enterprise Buying Committee Has Changed
Enterprise SaaS rarely has a single buyer anymore.
You may have:
- The end user who wants the product.
- The functional leader who owns the budget.
- IT evaluating architecture.
- Security evaluating risk.
- Legal evaluating contracts and data processing.
- Procurement negotiating commercial terms.
- Finance looking at ROI.
- The executive sponsor asking whether the investment is strategically important.
Marketing often focuses heavily on the first three.
The deal can still die with the next four.
That's why security needs to move upstream.
If your marketing creates demand but does nothing to help a champion navigate internal approval, you've only solved half the buying problem.
---
The New Enterprise Marketing Question
The traditional SaaS marketing question is:
"How do we get more people to try the product?"
The enterprise question is increasingly:
"How do we make it easier for the right organization to say yes?"
That's a very different problem.
And it changes what marketing should build.
Instead of only creating:
- Product demos
- Free trials
- Feature pages
- Case studies
- ROI calculators
You also need:
- Trust centers
- Security documentation
- Data-flow explanations
- AI governance information
- Compliance documentation
- Data residency details
- Privacy commitments
- Clear explanations of third-party model usage
- Security questionnaires
- Architecture diagrams
None of this is particularly sexy.
But neither is a procurement delay.
---
Three Pillars of Security-Led Growth
A practical SLG strategy can be built around three areas.
1. Make Security Visible
Most SaaS companies still hide their security information behind a generic /security page.
There's usually a collection of certification logos, a few paragraphs about encryption, and a contact form.
For enterprise buyers, that's not enough.
Your website should answer the questions buyers are already asking.
Where is data stored?
How is it encrypted?
Who can access it?
What happens to customer data when AI features are used?
What third-party services touch the data?
What are your retention policies?
Which compliance frameworks do you support?
Can customers control their encryption keys?
Can a security professional get the documentation without starting a six-email conversation with an SDR?
These aren't merely security questions.
They're conversion questions.
If a buyer cannot find the answer, they don't necessarily conclude that the answer is "no."
They may simply conclude that working with you will be difficult.
---
2. Turn Trust Into Marketing Proof
There's a big difference between saying:
"Enterprise-grade security."
And proving what that actually means.
Enterprise buyers have become increasingly skeptical of vague claims.
The same applies to AI.
"AI-powered."
"Enterprise AI."
"Secure AI."
"Responsible AI."
These phrases don't mean much without evidence.
A stronger approach is to explain the architecture.
For example:
- What data enters the system?
- What data leaves it?
- Which models process it?
- Is customer data retained?
- Is it used for model training?
- Where are inference workloads processed?
- What controls exist between customers?
- Who owns encryption keys?
- What gets logged?
- How long are logs retained?
This is where marketing and engineering need to work together.
Marketing shouldn't invent security claims.
Engineering shouldn't be expected to turn architecture diagrams into compelling buyer communication.
The CMO's job is to connect the two.
---
3. Give the Champion a "CISO Fast Pass"
Here's one of the most practical SLG ideas.
Don't make your champion do all the work.
If someone inside an enterprise wants to buy your software, give them everything they need to defend that decision internally.
Call it a CISO Fast Pass, an Enterprise Trust Kit, or whatever fits your brand.
The name matters less than the contents.
It could include:
- Completed security questionnaires where possible.
- Data-flow diagrams.
- Architecture documentation.
- Encryption details.
- Data-processing information.
- AI model and data-retention policies.
- Compliance documentation.
- Standard contractual information.
- Privacy documentation.
- A concise executive security summary.
The goal is simple:
Make your champion look smart for choosing you.
That's a powerful form of marketing.
---
Security Shouldn't Be a Sales-Stage Surprise
One of the biggest mistakes I see in enterprise GTM is treating security as a handoff.
Marketing generates the lead.
Sales qualifies the opportunity.
The demo happens.
The buyer gets excited.
Then someone says:
> "Great. Now we need to send you our security questionnaire."
Suddenly, momentum disappears.
The champion has to involve another team.
Security has questions.
Legal has questions.
Architecture has questions.
The vendor's AE starts chasing documents.
Two weeks become four.
Four become eight.
The champion gets distracted.
The competitor gets another meeting.
Eventually, the deal becomes "still under review."
This is where security becomes a sales tax.
But it doesn't have to be.
If you surface trust information earlier, you can turn the same process into a differentiator.
Instead of:
"We'll send the security documentation when you ask."
You can say:
"Here's everything your security and procurement teams are likely to need."
That is a very different buying experience.
---
The Trust Center Should Be a Growth Asset
A modern enterprise Trust Center shouldn't exist simply because the security team asked for one.
It should be treated as a marketing asset.
Think about the buyer journey.
Someone hears about your company.
They search for you.
They visit your website.
They look at the product.
Then they Google:
"[Company] security"
or
"[Company] SOC 2"
or
"[Company] data privacy"
or
"[Company] AI security."
Those searches are not necessarily coming from security teams.
They may come from prospects, IT leaders, procurement teams, analysts, or executives.
Your trust content is therefore part of your digital buying experience.
It deserves the same attention you give your product pages.
---
The AI Question Makes This Even More Important
AI has made the trust conversation harder.
Enterprise buyers increasingly need to understand not only what your software does, but what happens to their information when AI is involved.
This is where many SaaS companies fall into what I would call AI-washing.
They lead with impressive AI language without explaining the underlying data architecture.
That creates curiosity at the top of the funnel.
But it can create friction later.
The better approach is straightforward:
Don't just market the intelligence. Market the boundaries.
Tell buyers:
- What the AI can access.
- What it cannot access.
- What is stored.
- What isn't stored.
- Which models are used.
- How third-party providers are handled.
- Whether customer data is used for training.
- What customers can control.
In enterprise marketing, constraints can actually build confidence.
The buyer doesn't need you to claim that your AI is magical.
They need to know that it is governable.
---
What This Means for the CMO
This is where SLG becomes more than a security initiative.
It becomes a marketing operating model.
The CMO should be asking:
Is security content part of our demand-generation strategy?
If security information only appears after a prospect becomes an opportunity, you're already late.
Can a buyer self-educate?
If every security question requires an SDR, AE, or solutions engineer, you're creating unnecessary friction.
Can our champion defend us internally?
Your best advocate may need to convince five other people that buying your product is safe.
Help them.
Are our AI claims backed by architecture?
If the marketing story and technical reality don't line up, enterprise buyers will find the gap.
Are we measuring security-related sales friction?
Track where opportunities slow down.
Track how long reviews take.
Track which objections appear repeatedly.
Then work with Sales, Security, Product, and Legal to remove those obstacles.
---
The Metrics I Would Actually Watch
I wouldn't build an SLG dashboard with dozens of vanity metrics.
I'd start with a handful of questions.
1. Security Review Duration
How long does it take an opportunity to move from security review to approval?
If that number is falling, you're removing friction.
2. Sales Cycle Length
Compare deals where trust information was available early with deals where it appeared late.
The difference can tell you whether your SLG investment is actually helping.
3. Enterprise Win Rate
Are opportunities with stronger trust engagement converting at a higher rate?
Look for patterns rather than assuming causation.
4. Security-Related Deal Slippage
How many deals move out of the quarter because of security, privacy, legal, or compliance questions?
This is a metric the CFO will understand.
5. Trust Center Engagement
Which trust resources are prospects actually consuming?
If your architecture page is one of the most visited pages among enterprise opportunities, that's useful commercial intelligence.
---
The Bigger CMO Opportunity
The most interesting part of Security-Led Growth isn't really security.
It's risk reduction as a growth strategy.
Enterprise buyers don't only want better software.
They want fewer reasons to regret buying it.
That's why trust can become a competitive advantage.
Two vendors might offer similar functionality.
One requires:
- Multiple security calls
- Manual questionnaires
- Weeks of documentation requests
- Repeated explanations about AI data handling
- Legal back-and-forth
The other has:
- A transparent Trust Center
- Clear architecture
- Self-serve documentation
- Straightforward AI governance
- Pre-prepared security materials
- A champion-ready internal business case
The products may be comparable.
The buying experiences aren't.
And in enterprise SaaS, the easier company to buy often has an advantage over the better product.
---
So, Is SLG Replacing PLG?
Not really.
The better way to think about it is that enterprise GTM is becoming more hybrid.
PLG helps people discover and experience the product.
Sales helps organizations understand the business case.
Security-Led Growth helps organizations become comfortable with the risk.
The strongest enterprise companies can connect all three.
The goal isn't to put a security questionnaire at the top of your funnel.
It's to make trust part of the reason buyers are comfortable moving forward.
---
The CMO Takeaway
If you're selling enterprise SaaS, I'd stop thinking about security as something that happens after marketing has done its job.
Security is increasingly part of the buying experience marketing is responsible for shaping.
Your product still needs to be great.
Your positioning still needs to be sharp.
Your demand generation still needs to work.
But when your average contract is worth tens or hundreds of thousands of dollars, trust is part of the value proposition.
The companies that understand this will make security easier to buy.
And that can become a genuine growth advantage.
The future of enterprise GTM isn't just product-led. It is trust-enabled.
---
Final CMO Perspective
Security used to be something you proved when the buyer asked.
In enterprise SaaS, I think the smarter strategy is to make trust visible before they have to ask.
Because when the product experience is increasingly easy to replicate, the confidence you create around the product becomes part of the moat.
FAQ
What is Security-Led Growth (SLG)?
Security-Led Growth is a B2B go-to-market approach that brings security, privacy, compliance, data governance, and technical trust into the buying journey earlier. Instead of treating security as a late-stage procurement requirement, SLG makes trust part of marketing, positioning, and demand generation.
Is Security-Led Growth replacing Product-Led Growth?
Not necessarily. PLG remains useful for product discovery and adoption. Security-Led Growth addresses a different problem: helping enterprise organizations evaluate and approve the risk associated with adopting the product.
Why is security becoming more important in enterprise SaaS sales?
Enterprise software increasingly handles sensitive business data and incorporates AI, APIs, cloud infrastructure, and third-party services. As a result, buyers often need security, privacy, legal, and compliance teams involved before they can approve a purchase.
What should a B2B SaaS Trust Center include?
A strong Trust Center can include security architecture, encryption practices, compliance documentation, data residency information, privacy policies, AI governance, data-retention policies, third-party subprocessors, certifications, and relevant security documentation.
What is a CISO Fast Pass?
A CISO Fast Pass is a collection of security and compliance materials designed to help an internal champion move a SaaS purchase through their organization's security review. It can include security questionnaires, architecture diagrams, data-flow documentation, privacy information, compliance documentation, and contractual materials.
How can CMOs measure Security-Led Growth?
Useful metrics include security-review duration, overall sales-cycle length, security-related deal slippage, enterprise win rate, trust-center engagement, and the percentage of opportunities that access security resources before formal procurement begins.
Does Security-Led Growth only apply to cybersecurity companies?
No. Any B2B SaaS company selling into organizations with meaningful security, privacy, compliance, or data-governance requirements can benefit from the approach. The larger and more regulated the customer, the more important the buying experience around trust becomes.
In enterprise SaaS, the next growth advantage may not be a better product, it may be making that product easier to trust and easier to buy. Let's Talk.